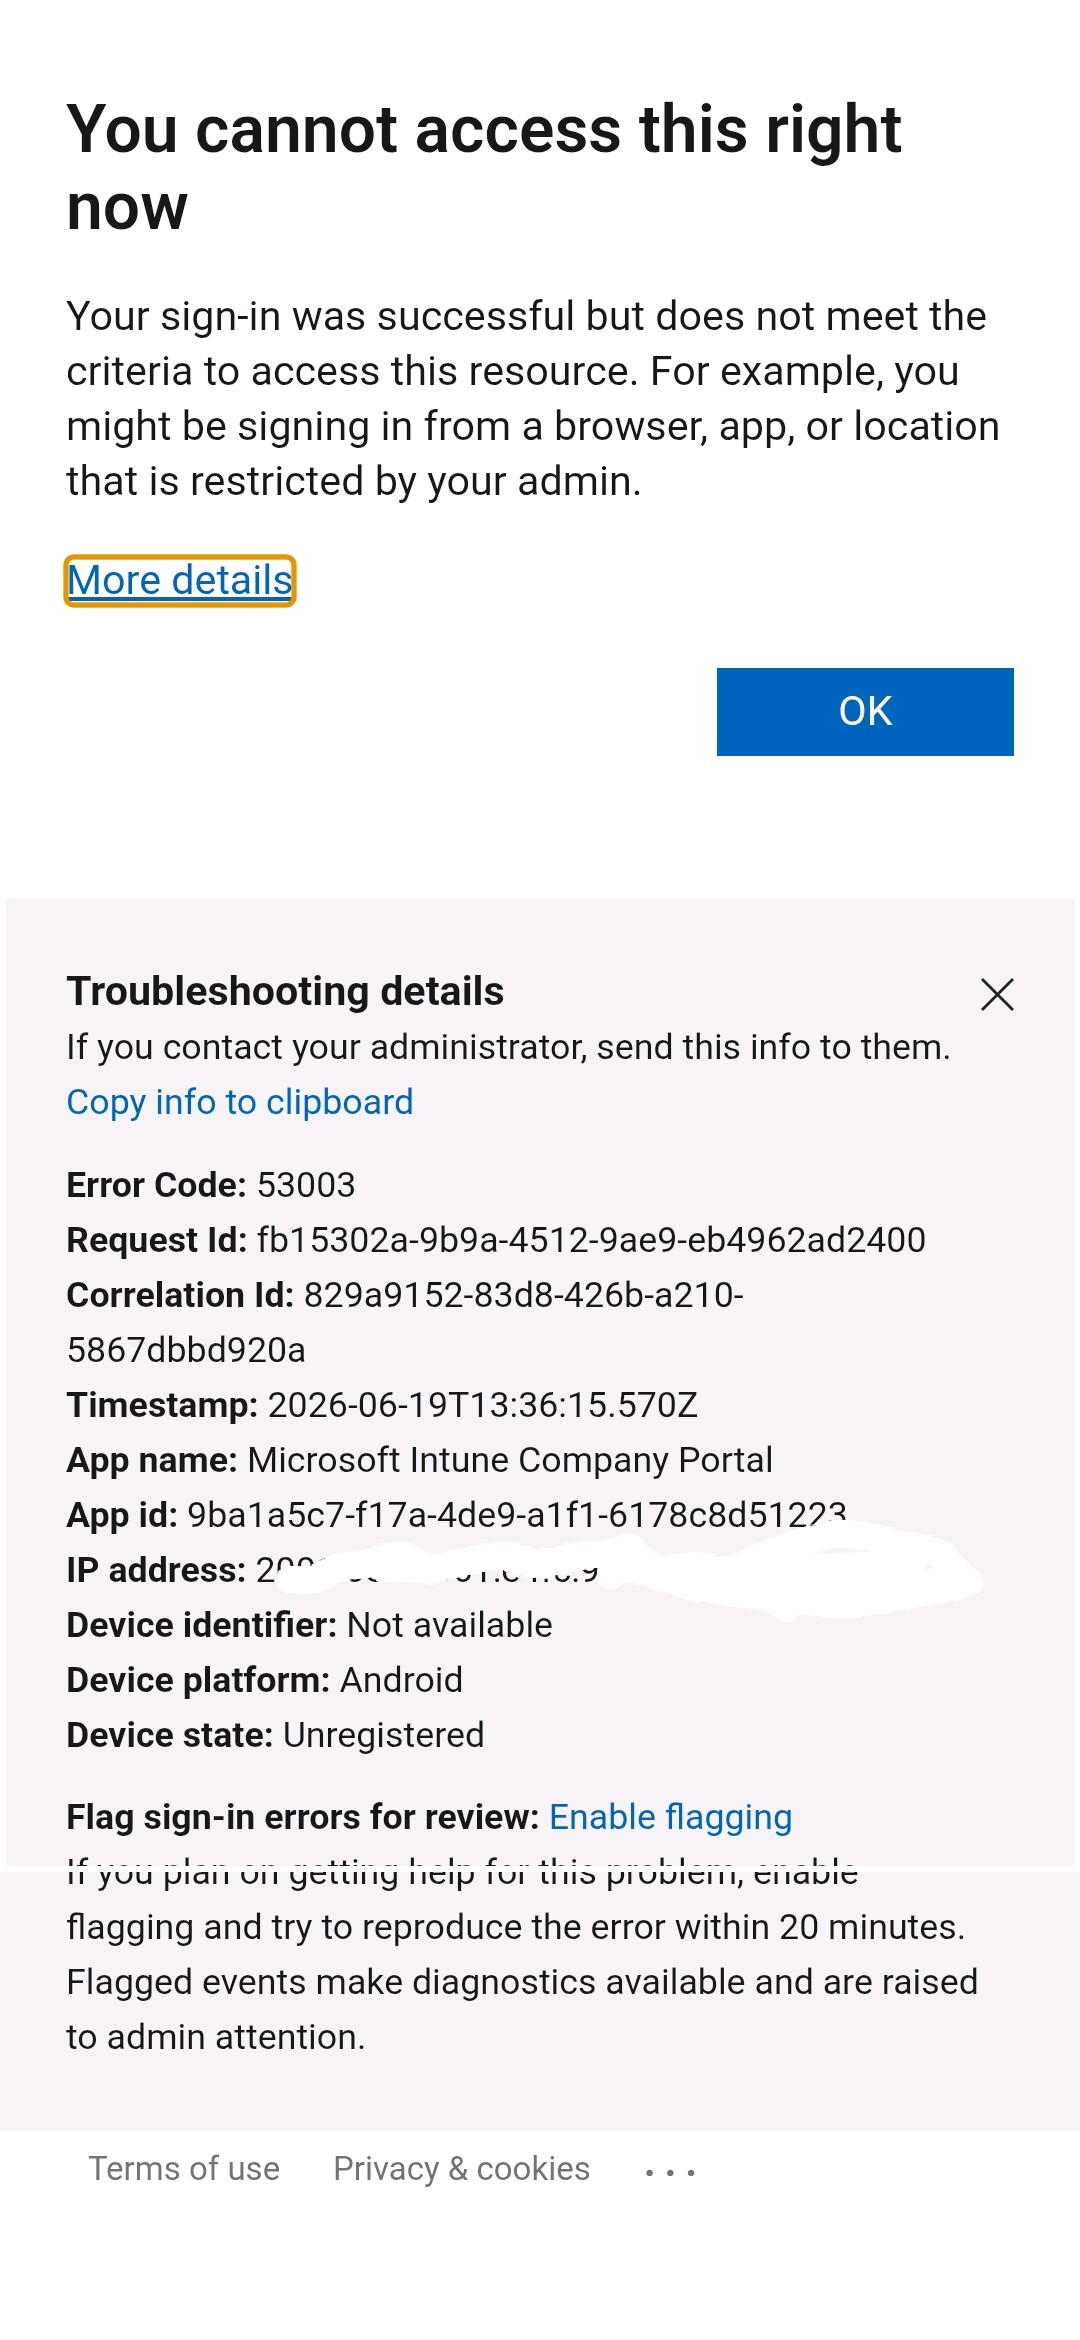
With every new release, I curiously check whether the broken MS Intune Company Portal / MS Teams integration has been fixed again.
There are multiple related threads and GitLab issues, all of them have been closed in the meanwhile. But I cannot find an explicit statement from /e/OS saying we won’t fix it in the near future.
Could you maybe ask someone from the team whether this has any priority? If not, that’s also okay and understandable for me, taking into account that targeting the right priorities is a delicate dance. But such a statement would provide some clarity - in my case, for example, I would buy a used older phone using Google Android and install the stuff there.
I have tried every solution I could find online, no luck. But… my tries (also with help of Lumo) gave me an idea… download the apk from the Microsoft site directly. That solved the matter: intune is installed, a work profile active and I can now install teams, outlook and all the apps I need for work.
As @Ludix suggests, these error messages arrise when (as the text explains) you have provided correct authentication, but the administrator has not deemed that the device (or the setup of the environment on it) should be allowed to sign in. Your device or OS might not be on an allow list, for example.
Thank you for your engagement and the community’s support so far. I really appreciate the effort everyone is putting into troubleshooting.
However, my main concern is not about workarounds or company policies. The issue is that MS Intune and MS Teams integration used to work on /e/OS but broke after a specific release. This suggests a regression in /e/OS or microG itself, not just a compatibility issue with my organization’s IT setup.
My question to the /e/OS team is simple:
Is this something /e/OS plans to address as part of its focus on business usability? Or is it not a priority for the project at this time?
A clear statement—whether it’s a “yes, we’re working on it” or a “no, this isn’t in our current roadmap”—would help me and others make informed decisions about using /e/OS in professional environments.
Thank you for your time and for considering this request.
The issue is not closed it has been marked confidential. There has been no update or comment in it. If you have created the issue, you should be able to view it. You can add details to it and I would request the team to look into it and add their comments.
Issues where users do not update comments from their side are assumed as closed by the developer. Unless the users add some comments on the testing against latest releases the developers would not get an indication on the issues still being active.
I’ve added the following comment - is that sufficient for the team to look into the issue? And would it be easier for you to keep track of it if I created a similar comment upon every /e/OS release?
And what did the developers say? Is that something that they see as being tackled in the short run, so that it’s worth waiting for me? Or should I better try to find a Google Android burner phone and install the MS stuff there?
Hi,
At my employer I’m responsible for Conditional Access and Intune, and what this error usually means is that one of the required conditions isn’t met, which results in access being blocked. I recommend contacting your IT department and providing them with the correlation ID shown in the message. With that information they can determine exactly why access is being denied, and it may also help the e/OS developers troubleshoot the issue.
That said, Intune with a work profile enabled is working fine on my phone. The only thing currently failing for me is the Google Security check, unfortunately.