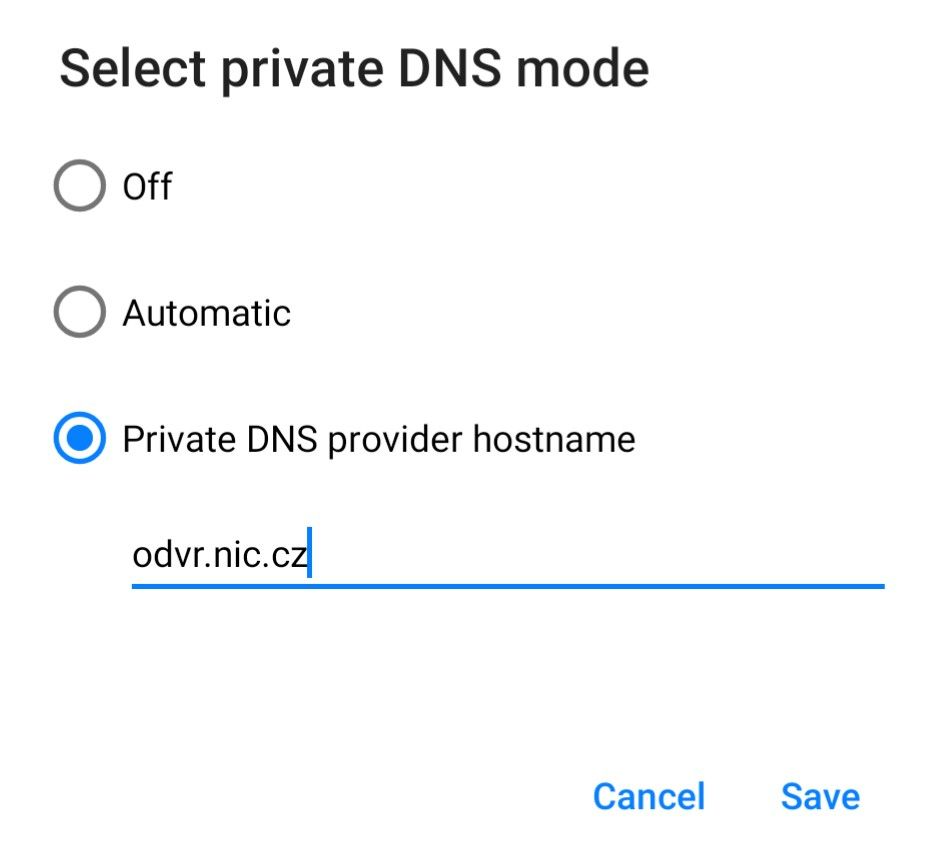
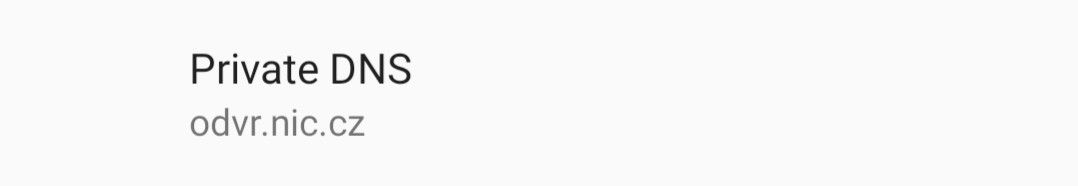
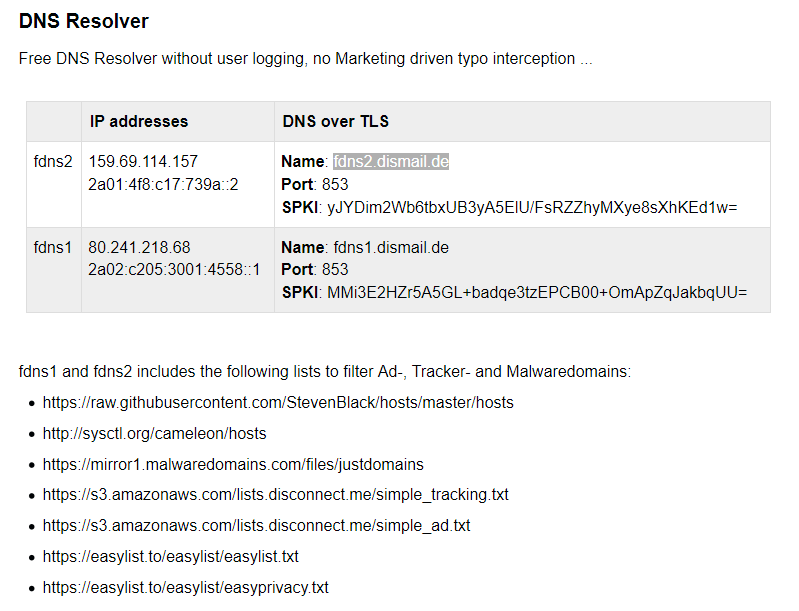
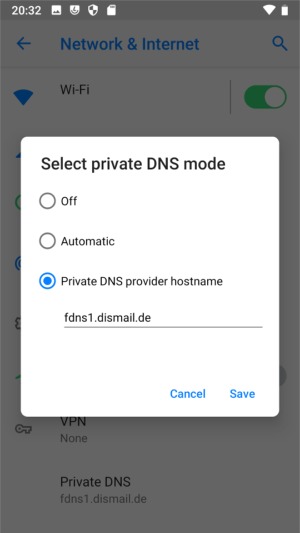
Learn to encrypt your DNS queries using DNS-over-TLS client implementation known as Private DNS in your smartphone running latest /e/OS.
Prerequisites:
A smartphone with /e/OS based on Android 9 or newer.
Patience to fiddle around with /e/OS Settings
Let’s roll.
Why should you Encrypt your DNS?
The same reason why we use https to access our favorite websites including this very forum or wiki. To seek privacy, security and integrity of data communication.
1. Goto /e/OS Settings to open Network & Internet settings therein.
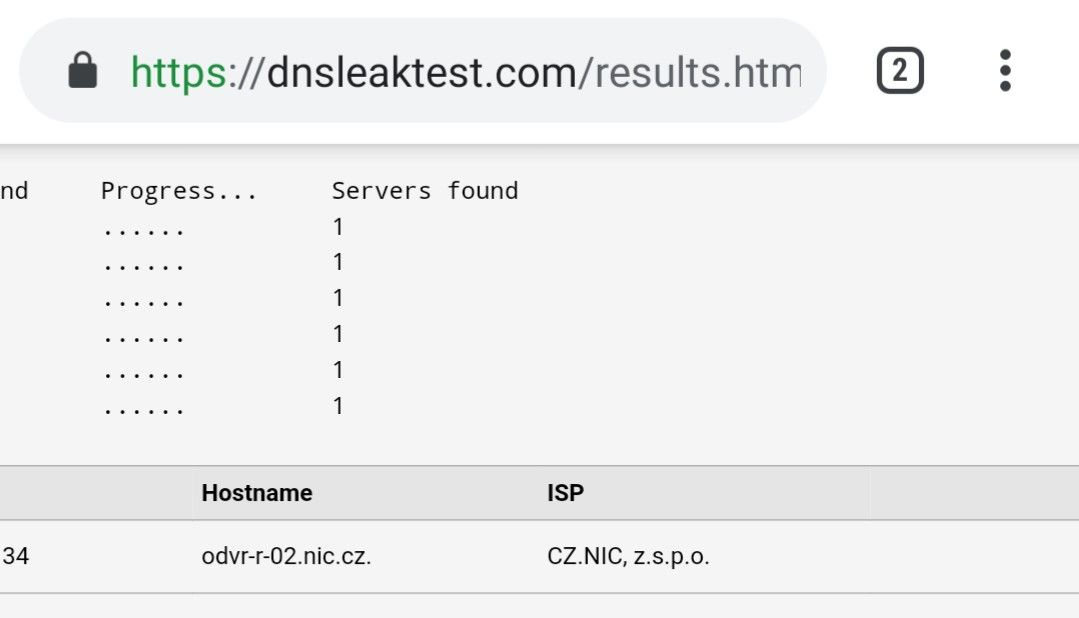
Once the test is complete you should exclusively see the DNS servers that you have set in Private DNS settings of your /e/OS, as seen in the image below.
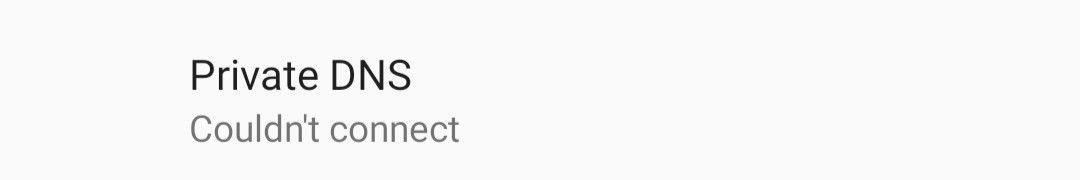
If you see the error as seen in the image above, it means you have entered wrong DNS hostname or the service you are using is broke. Try another one to check. It should fix the issue.
Also if you force DNS servers in Settings->Network & internet->DNS, like 9.9.9.9, you can set private DNS to automatic and it should use DNS over TLS using this server.
Note that with Quad9, DNS servers tested with dnsleaktest will show up as Woodynet (they have a partnership)
Just gotten the confirmation from the Dev of TrackerControl. TrackerControl can’t handle private DNS nor encrypted DNS requests.
TC is moste like Netguard, so I think (but don’t know for sure) that NG will also fail with this setup. So everyone have to decide: Blocking trackers or using private DNS encryption
It’s good you’re dealing with it, @harvey186 This information is valuable.
I appreciate the “Select private DNS mode” feature in /e/ OS 9-Pie and use it because with FOSS apps à la Simple Mobile Tools (/from F-Droid Store) and don’t need apps like the very attractive TrackerControl (TC).
That’s the best way, but for all other users which are using non-FOSS apps it a needed information that TC isn’t failing with private DNS and I have jus read (in german) that Netguard does have the same issue Blokada seems also onyl AFW+ with root not. But root is not the best for a device
And I quote securedns.eu in two postings (here and here) saying “Please do not use SecureDNS anymore.” So that should take care of that point.Or what do you think is necessary in order to be able to consider the subject as clarified?